Threat Intelligence

FTP Banner Dead Drops: A Hunter’s Field Guide to E4del and PINHOLE

THREAT INTELLIGENCE REPORT  Prepared by   Essa Amous, CTO, RST Cloud  Reporting date   10 September 2026  Introduction  This article builds on the original research published by SOCRadar, which identified a Windows malware delivery campaign using FTP server banners as dead-drop resolvers to distribute the E4del and PINHOLE remote access trojans.Rather than embedding a fixed payload location […]

FTP Banner Dead Drops: A Hunter’s Field Guide to E4del and PINHOLE Read More »
TencShell and Gshell

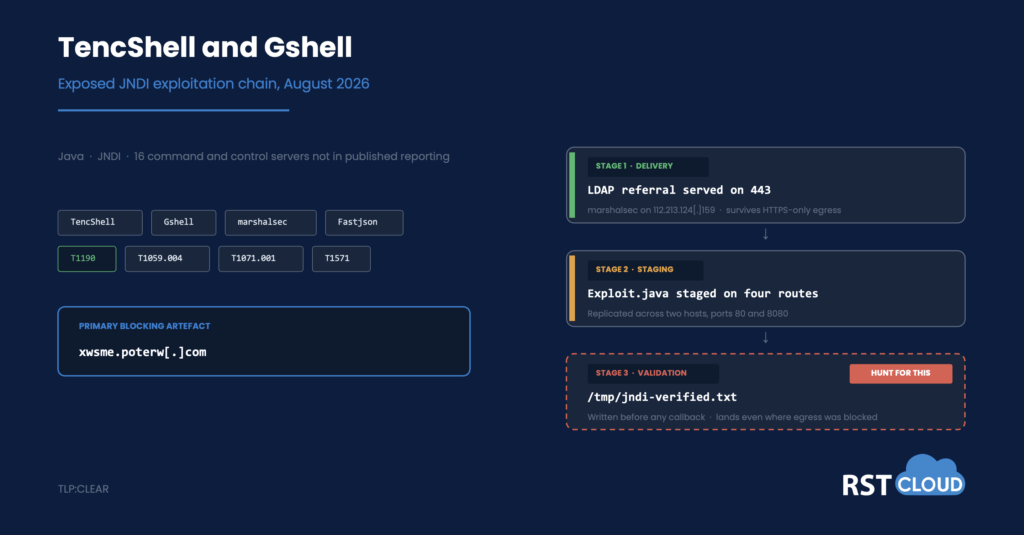
TencShell and Gshell

THREAT INTELLIGENCE REPORT  Prepared by   Alexander Gould, CTI Strategist, RST Cloud  Reporting date   17 August 2026  Collection   Scan-derived figures are as at 10 August 2026 Active infrastructure and an exposed exploitation chain Summary  Suspected China-linked operators are running an intrusion campaign against government bodies in Taiwan, Thailand, Afghanistan and the United States, and against billing

TencShell and Gshell Read More »

SLCyber logo

Searchlight Cyber Expands Threat Intelligence Solution with RST Cloud Integration

New partnership brings continuously updated threat intelligence from thousands of reports directly into Searchlight Threat, eliminating hours of manual research Portsmouth, UK, September 01 2026 – Searchlight Cyber today announced a strategic partnership with RST Cloud, a provider of AI-driven Cyber Threat Intelligence (CTI) solutions, to integrate the RST Threat Library, RST Threat Feed and

Searchlight Cyber Expands Threat Intelligence Solution with RST Cloud Integration Read More »